 RockCloud-基石云安全-官方博客
In the current cybersecurity landscape, many operations managers tend to focus on dealing with "high-volume" DDoS attacks, as Tbps-level flood attacks are the most intuitive and lethal. However, with the proliferation of AI technology, application-layer (Layer 7) threats against businesses are becoming increasingly stealthy and destructive.
The "Shadow" Beyond Traffic: Evolution of Application-Layer Attacks
If DDoS is "smashing the door," then application-layer attacks are "picking the lock."
Recent industry trends show a significant increase in automated vulnerability exploitation targeting API interfaces, AI services, and payment modules. Attackers no longer solely aim to exhaust bandwidth but use scanners to find SQL injection, cross-site scripting (XSS), or command execution vulnerabilities, intending to obtain sensitive data, hijack accounts, or perform malicious scraping. Moreover, many low-frequency, "slow CC attacks" that mimic real user behavior are constantly bypassing traditional static threshold policies.
In such scenarios, relying solely on edge high-defense CDN to block high traffic is insufficient. You need a "security expert" that can deeply parse HTTP/HTTPS request packets and understand business logic.
RockCloud Intelligent WAF: More Than Rule Matching
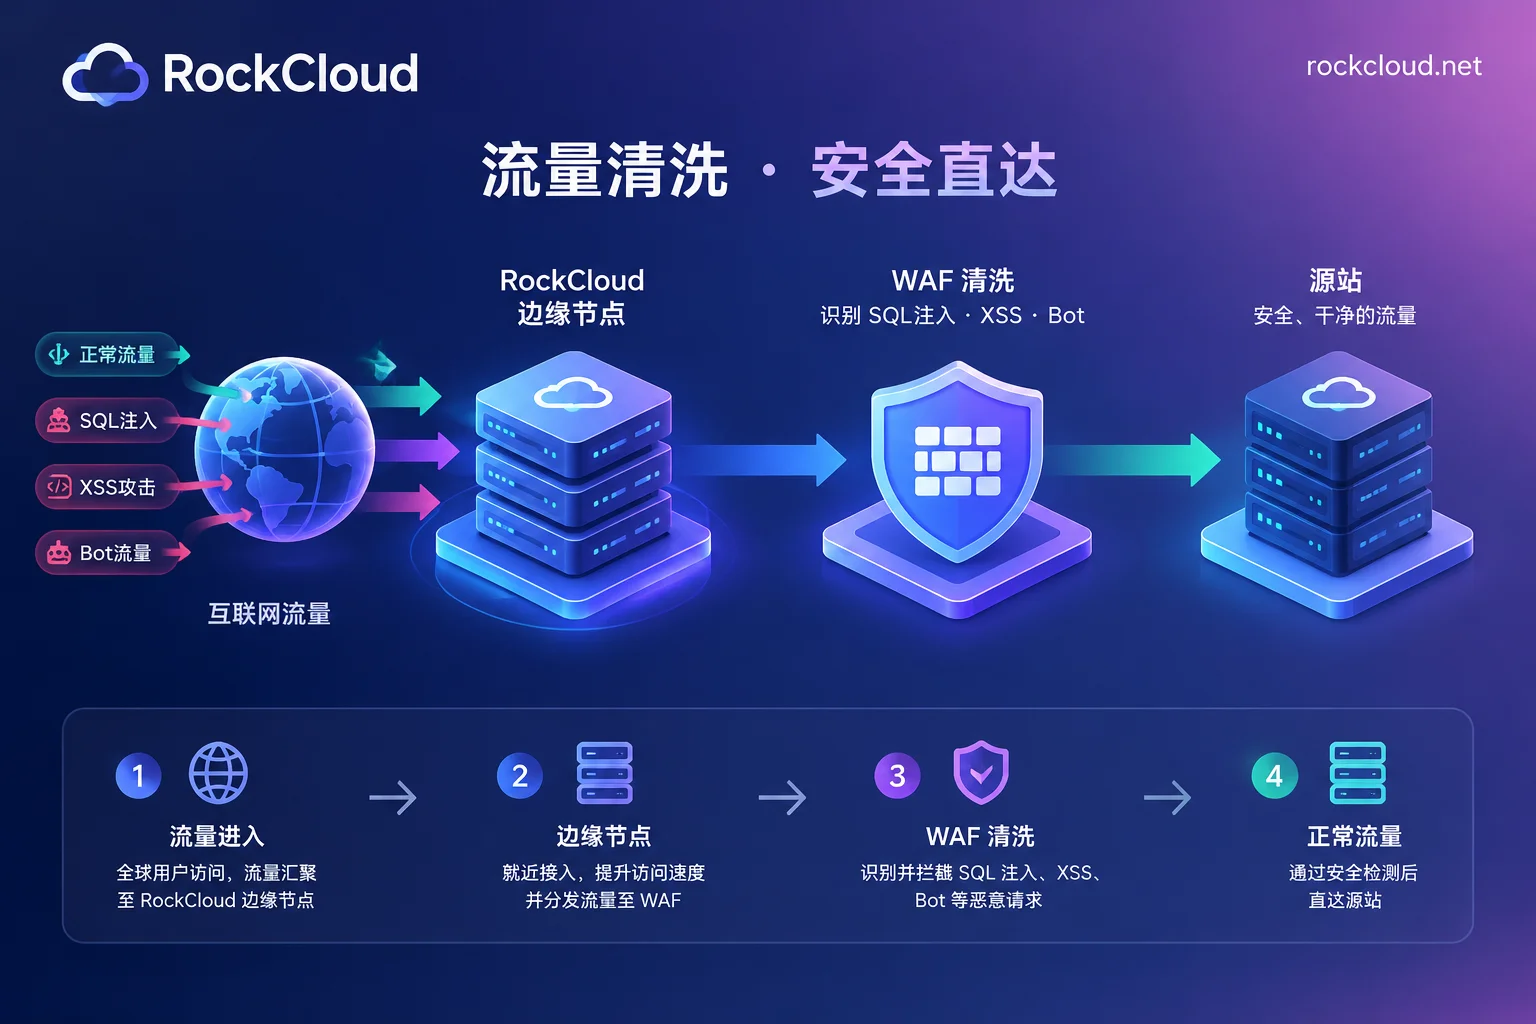
RockCloud's high-defense CDN not only provides customers with Anycast distributed scrubbing for DDoS defense but also incorporates a powerful intelligent WEB firewall (WAF). Our protection logic is not a simple stack of "blacklists" but builds a multi-dimensional security defense line:
- OWASP Core Rule Set as a baseline: Covers mainstream known threats such as SQL injection, file inclusion, and malicious script execution, intercepting mature attack methods immediately.
- Machine learning-enabled dynamic defense: For zero-day vulnerabilities not yet in rule sets or advanced variant attacks, our system uses machine learning to automatically identify malicious request patterns, achieving proactive warning and interception of unknown risks.
- One-click activation, seamless integration: Enable WAF with one click in the RockCloud control panel, without modifying complex origin code, perfectly fitting our convenient "CNAME access" process.
- Expert-assisted policies: For complex business logic, such as special security restrictions for payments or APIs, our security technical team can assist you in configuring fine-grained exception policies to ensure both business availability and security.
From "Passive Response" to "Proactive Defense"
In daily operations, we recommend treating security protection as part of the business architecture rather than a post-hoc patch. For how to build a more resilient architecture, you can refer to our previous best practices:
- API DDoS Protection Architecture: How to Respond to Multi-Vector Hybrid Attacks Without Blocking Legitimate Users
- Advanced CC Defense: Logical Strategies for Low-Frequency Slow Attacks and Residential Proxies
Security is Productivity
RockCloud always adheres to the concept of "defense and acceleration on the same link." This means you don't need to purchase an extra set of expensive security devices to deploy WAF, nor sacrifice security for performance. All defense policies take effect in real-time at our edge nodes.
Currently, we offer flexible billing methods and support on-demand testing. If your business is under attack, please contact us immediately through the Security Response Center or our Telegram channel for immediate protection support.


Comments(0)