RockCloud-基石云安全-官方博客
只是一个默认分类
API and Dynamic Interface CC Defense: Tackling Low-Frequency Slow Attacks, Residential Proxies, and High-Concurrency API Abuse
CC attacks increasingly use massive residential proxies to launch low-frequency slow requests, precisely targeting high-consumption dynamic interfaces such as APIs, login, search, and AI inference. This article analyzes why traditional static rate limiting and pop-up verification fail in API scenarios, and provides a CC defense solution that balances anti-abuse and business continuity by combining high-defense CDN, machine learning WAF, security tokens, and unlimited request billing.
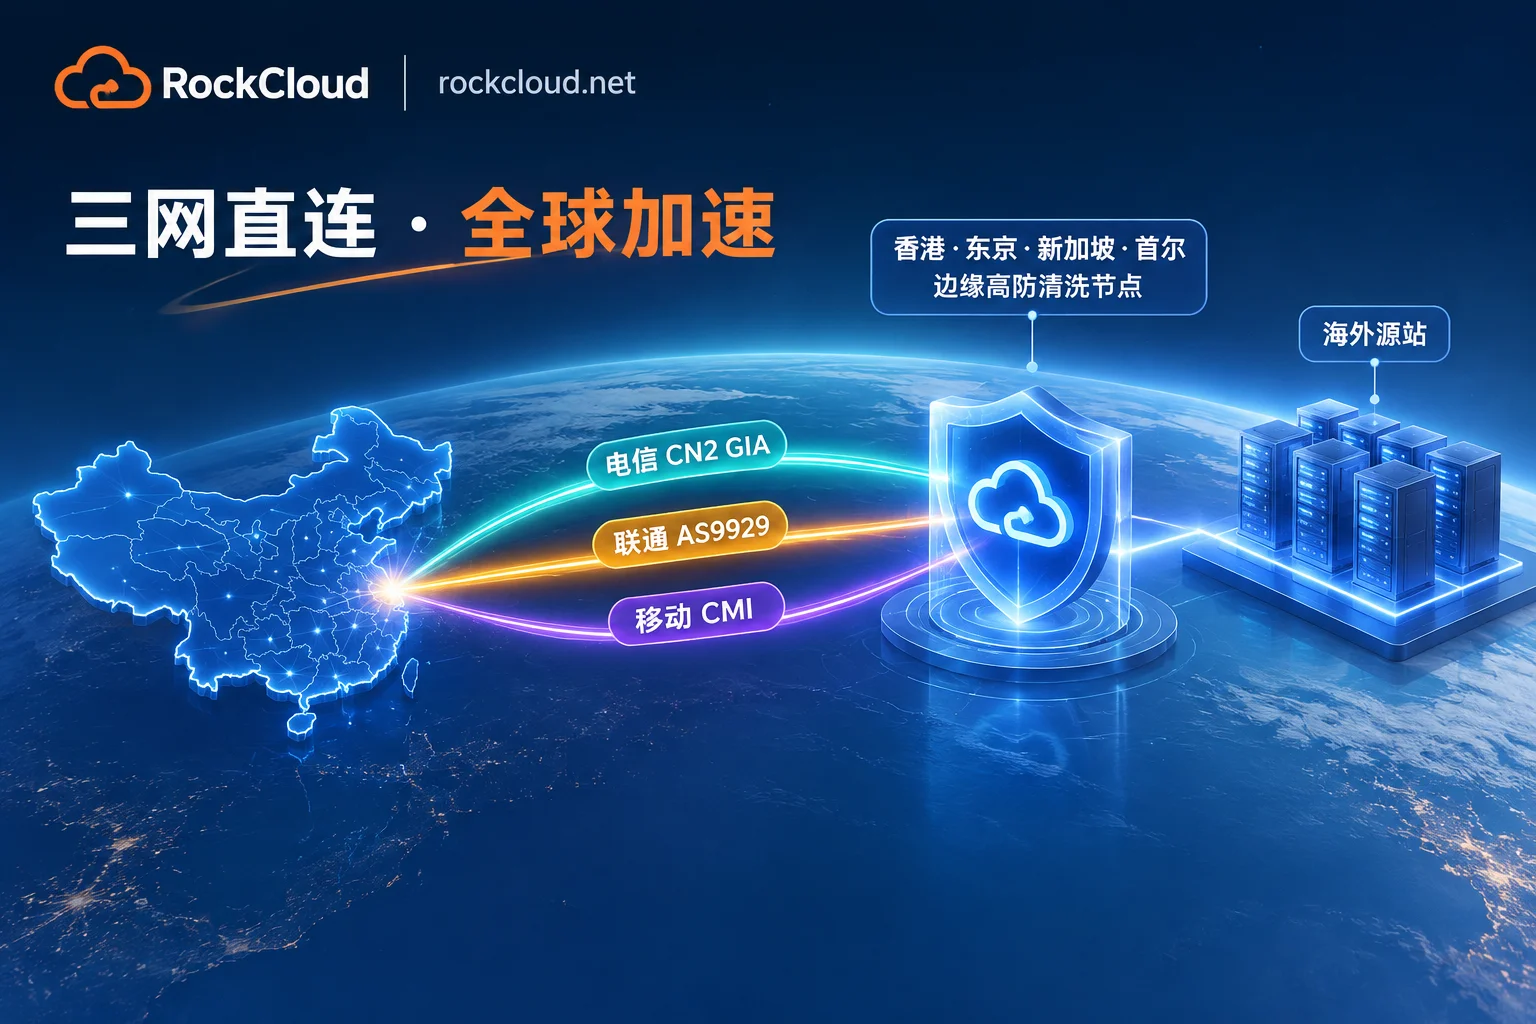
How to Implement CN2 Line Acceleration: Why a CN2 Server Alone Is Not Enough, and Why You Need Multi-Line Direct Connection and High-Defense CDN Archi
Many cross-border businesses serving mainland China find that even with expensive overseas CN2 servers, they still face peak-hour lag for China Unicom and China Mobile users, burst bandwidth limits, and blackholing under attack. This article analyzes from the underlying network routing and security architecture why decoupling the origin from the acceleration layer, and using ring-China nodes with Telecom CN2 GIA, Unicom AS9929, and Mobile CMI multi-line direct connections plus high-defense CDN, is the preferred solution balancing extreme speed and business continuity.
New Trends in Global Acceleration Networks: How to Achieve Ultra-Fast Cross-Border Access While Ensuring Business Security?
An analysis of the latest trends in global acceleration networks and how RockCloud's anti-DDoS CDN enables end-to-end security and access optimization for businesses facing dual needs of anti-DDoS protection and cross-border acceleration.
DDoS Attack Incoming: Don't Let Your Business Crash While 'Waiting for Response' — RockCloud Emergency Response Manual
When your business suffers a sudden DDoS attack, every second lost means lost users and revenue. This article summarizes an emergency avoidance guide during an attack and explores how RockCloud's high-defense CDN enables 'minute-level' rapid onboarding, hiding the origin server while integrating defense and acceleration to help your business run smoothly through the storm.
Bot Management: How to Use Edge WAF for Fine-Grained Traffic Control When AI Crawlers and Automated Scripts Flood Login and Payment APIs
In 2026, malicious bot traffic is growing more than 9 times faster than human traffic, and attacks are shifting from public page scraping to core business flows like login, shopping cart, and payment. This article combines the latest industry security reports to analyze why traditional static anti-scraping rules fail and shares how to implement an efficient bot management architecture using high-defense CDN, intelligent WAF machine learning, and custom rules from security teams.