RockCloud-基石云安全-官方博客
Which Businesses Are Suited for Hong Kong CN2 DDoS-Protected Servers: Three Scenarios, Two Limitations, and Common Architectures
Hong Kong CN2 DDoS-protected servers are best for businesses that meet three conditions: primary users in mainland China, sensitivity to latency and packet loss, and frequent DDoS or CC attacks. This article explains the selection priorities for gaming, financial and payment APIs, and overseas-facing independent websites, analyzes two limitations—high bandwidth costs and route switching after attacks exceed capacity—and provides three architectures: standalone, front-end DDoS-protected CDN, and game shield, along with questions to confirm before procurement.
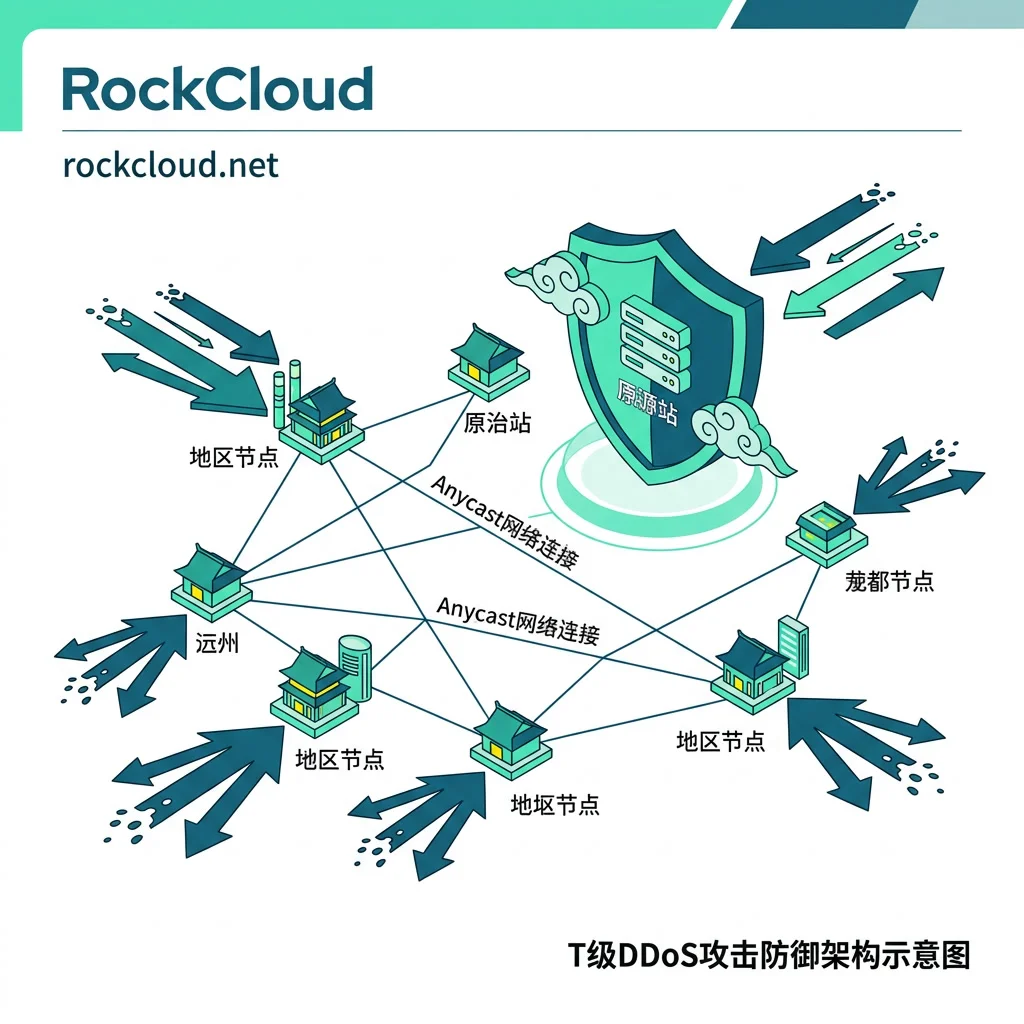
Architecture for Handling Tbps-Scale DDoS Attacks: Single Data Center or Multi-Region Edge Offload?
Handling Tbps-scale DDoS attacks requires distributed edge-based offload across multiple locations; a single data center will break at the upstream link first. This article breaks down the four-layer responsibilities and provides a selection comparison table and a self-check checklist.
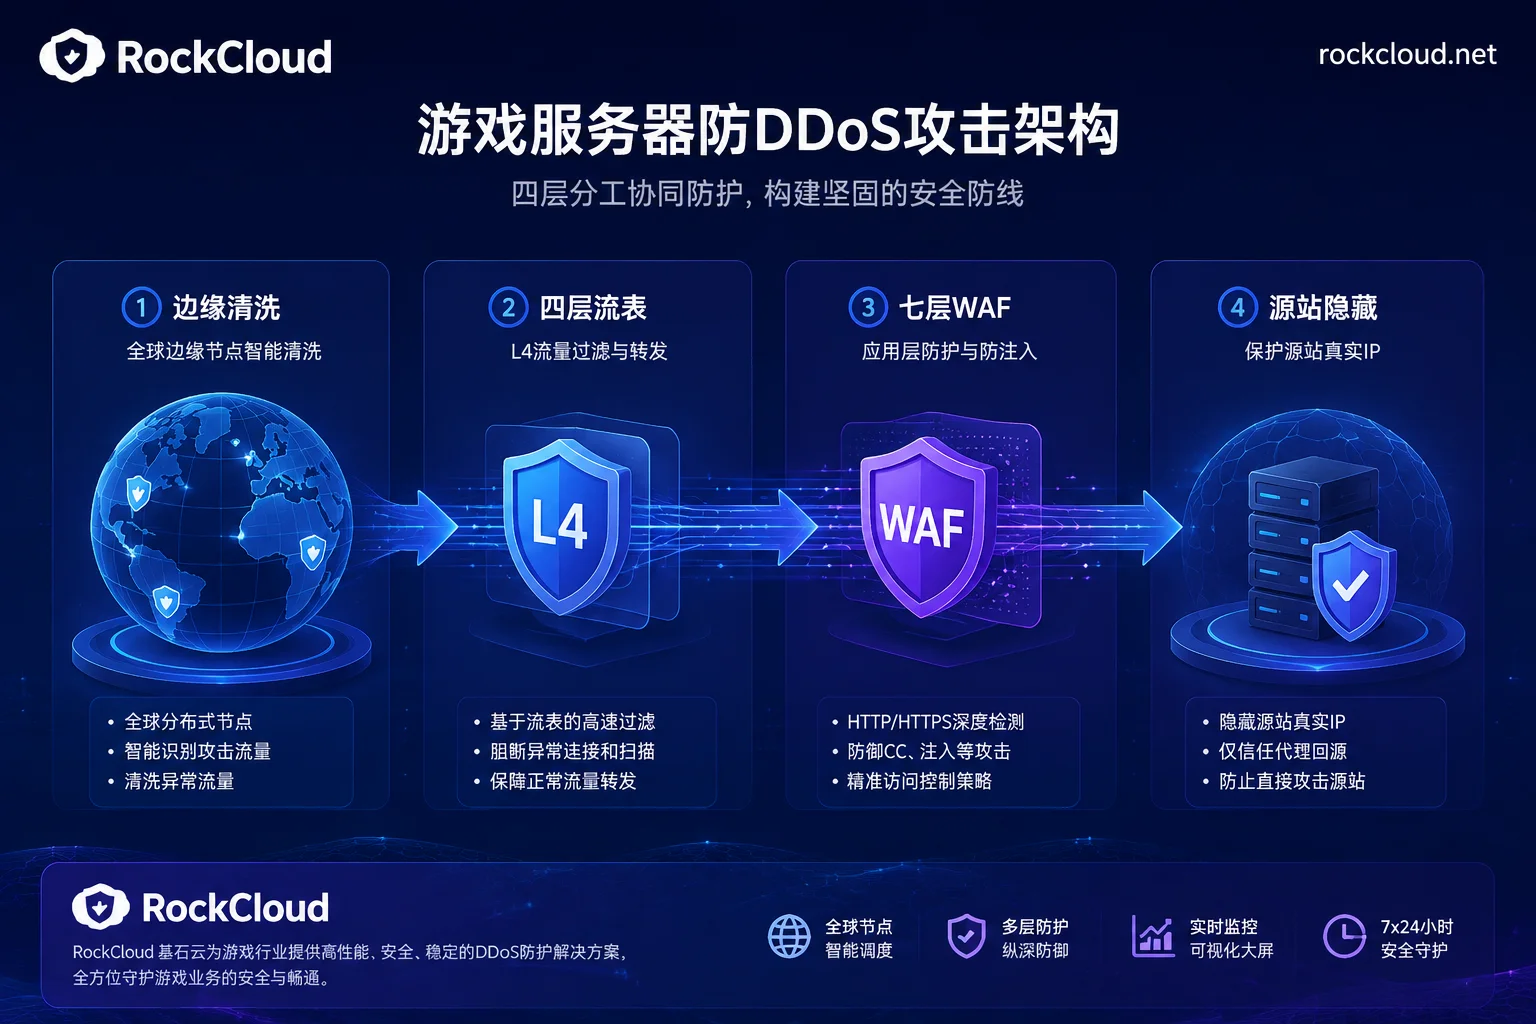
Game Server DDoS Defense Architecture: Four-Layer Division and Acceptance Criteria
When designing game server DDoS defense, first split traffic by type into four layers, then use acceptance criteria to validate each layer's effectiveness.