RockCloud-基石云安全-官方博客
In today's digital business, APIs are not just data transmission channels but the lifeline of business logic. Recent security industry research shows that the trend of attacks against APIs has undergone a qualitative change: traditional "brute force flooding" is transforming into "refined consumption," especially with AI-automated bot crawlers that can precisely hit business interfaces and consume backend computing resources.
Why Are Your APIs Easy Targets for Attackers?
Compared to traditional web pages, API interfaces typically lack human interaction, and their traffic patterns can be easily disguised as legitimate calls. Attackers use low-frequency, long-period requests to evade traditional threshold-based blocking, which means many enterprises, when under attack, often do not suffer from bandwidth saturation but from origin database crashes and surging API response delays, ultimately paralyzing business logic.
For Web API and AI service businesses, we recommend deeper defense strategies:
- Origin Cloaking and Link Scrubbing: Do not expose your origin server directly to the internet. Through RockCloud High-Defense CDN's Anycast distributed scrubbing, attack traffic is intercepted at the edge, ensuring the origin IP remains "invisible."
- Intelligent WAF and Behavioral Analysis: For AI crawlers and various malicious bots, static rules alone are insufficient. RockCloud's Intelligent WEB Firewall not only includes built-in OWASP rulesets but also introduces machine learning models to dynamically identify non-human abnormal access patterns and filter malicious traffic at the source.
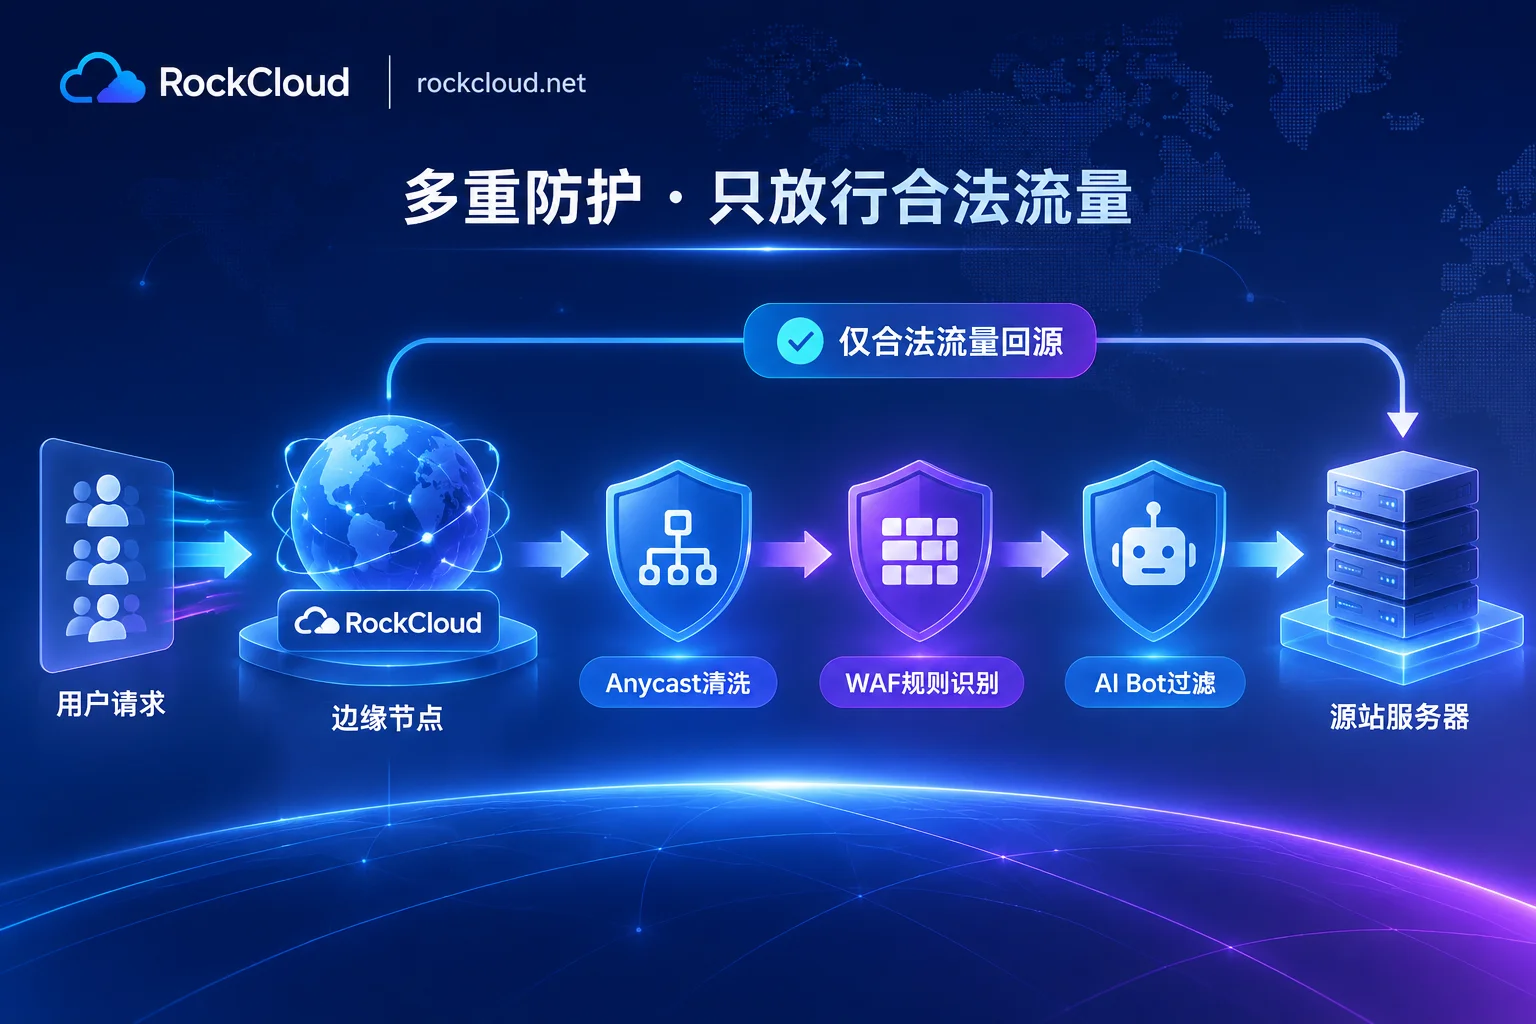
Building a "Deep" Defense Line That Withstands Consumption
Facing high-concurrency API flooding and distributed denial-of-service attacks, RockCloud's defense architecture emphasizes "one-stop protection":
- Integrated Delivery: Whether DDoS/CC defense or WAF, all are integrated on the same request path, eliminating the need to purchase multiple vendor products and reducing operational complexity.
- Full Protocol Coverage: In addition to standard HTTP/HTTPS APIs, for games or real-time services with special connection requirements, the Game Shield Solution provides private protocol encapsulation and edge forwarding to ensure uninterrupted connections.
- CN2 Dedicated Line Optimization: While defending against attacks, CN2 China Acceleration provides stable link assurance for cross-border businesses, balancing security and access speed.
How to Respond Immediately to Attacks?
Defense is not a post-mortem summary but continuous governance. We recommend selecting layers based on business characteristics; you can refer to our Solution Comparison to match the most suitable configuration. If your API is under attack, please contact us immediately via the Contact Page or Telegram Support for emergency response. We support seamless integration without modifying origin NS; a simple CNAME change enables quick switching.
If you still have concerns about routine API protection, you can refer to our in-depth analyses on API and Dynamic Interface CC Defense and Bot Management Strategies to optimize your defense architecture from the ground up.