RockCloud-基石云安全-官方博客
Which Businesses Are Suited for Hong Kong CN2 DDoS-Protected Servers: Three Scenarios, Two Limitations, and Common Architectures
Hong Kong CN2 DDoS-protected servers are best for businesses that meet three conditions: primary users in mainland China, sensitivity to latency and packet loss, and frequent DDoS or CC attacks. This article explains the selection priorities for gaming, financial and payment APIs, and overseas-facing independent websites, analyzes two limitations—high bandwidth costs and route switching after attacks exceed capacity—and provides three architectures: standalone, front-end DDoS-protected CDN, and game shield, along with questions to confirm before procurement.
How to Apply for a Free Trial of a High-Defense CDN: Materials, Onboarding Sequence, and Verification Points During the Trial Period
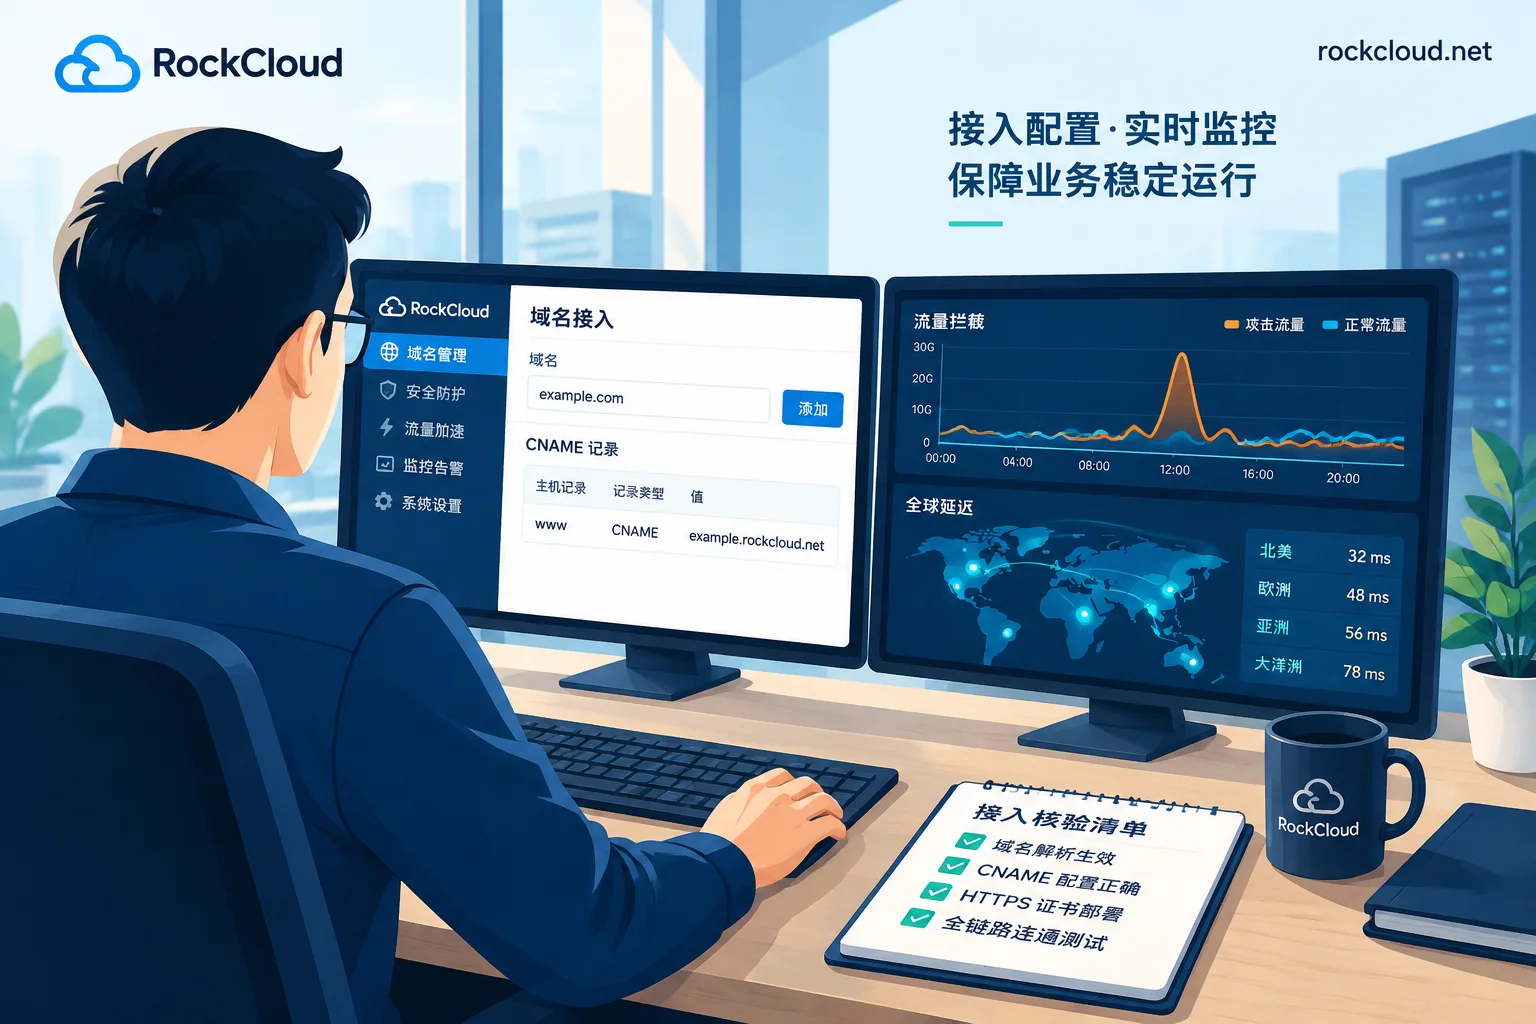
Applying for a free trial of a high-defense CDN: the real work lies in clearly describing your business, onboarding in the correct sequence, and verifying the right metrics during the trial window.
Does High-Defense CDN Require Changing NS: CNAME vs NS Activation Speed, Protection Boundaries, and Selection Criteria
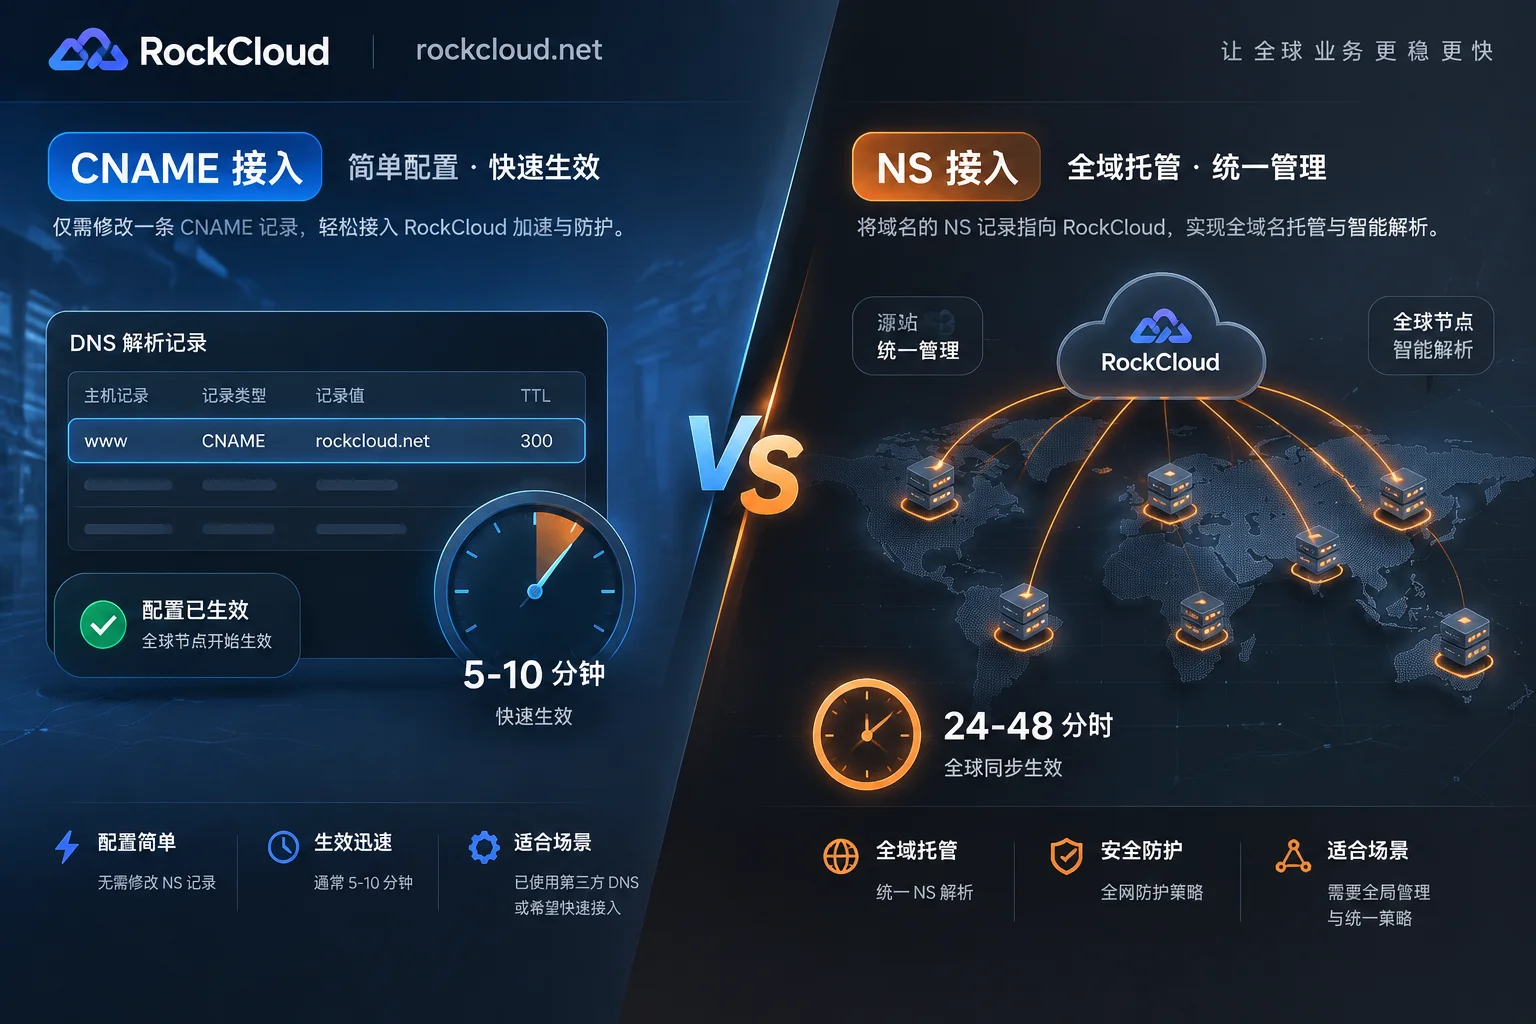
High-defense CDN access does not require changing NS records; CNAME access takes effect in minutes with limited protection scope, while NS access offers full-domain protection including DNS layer but requires hours to 48 hours to propagate globally.
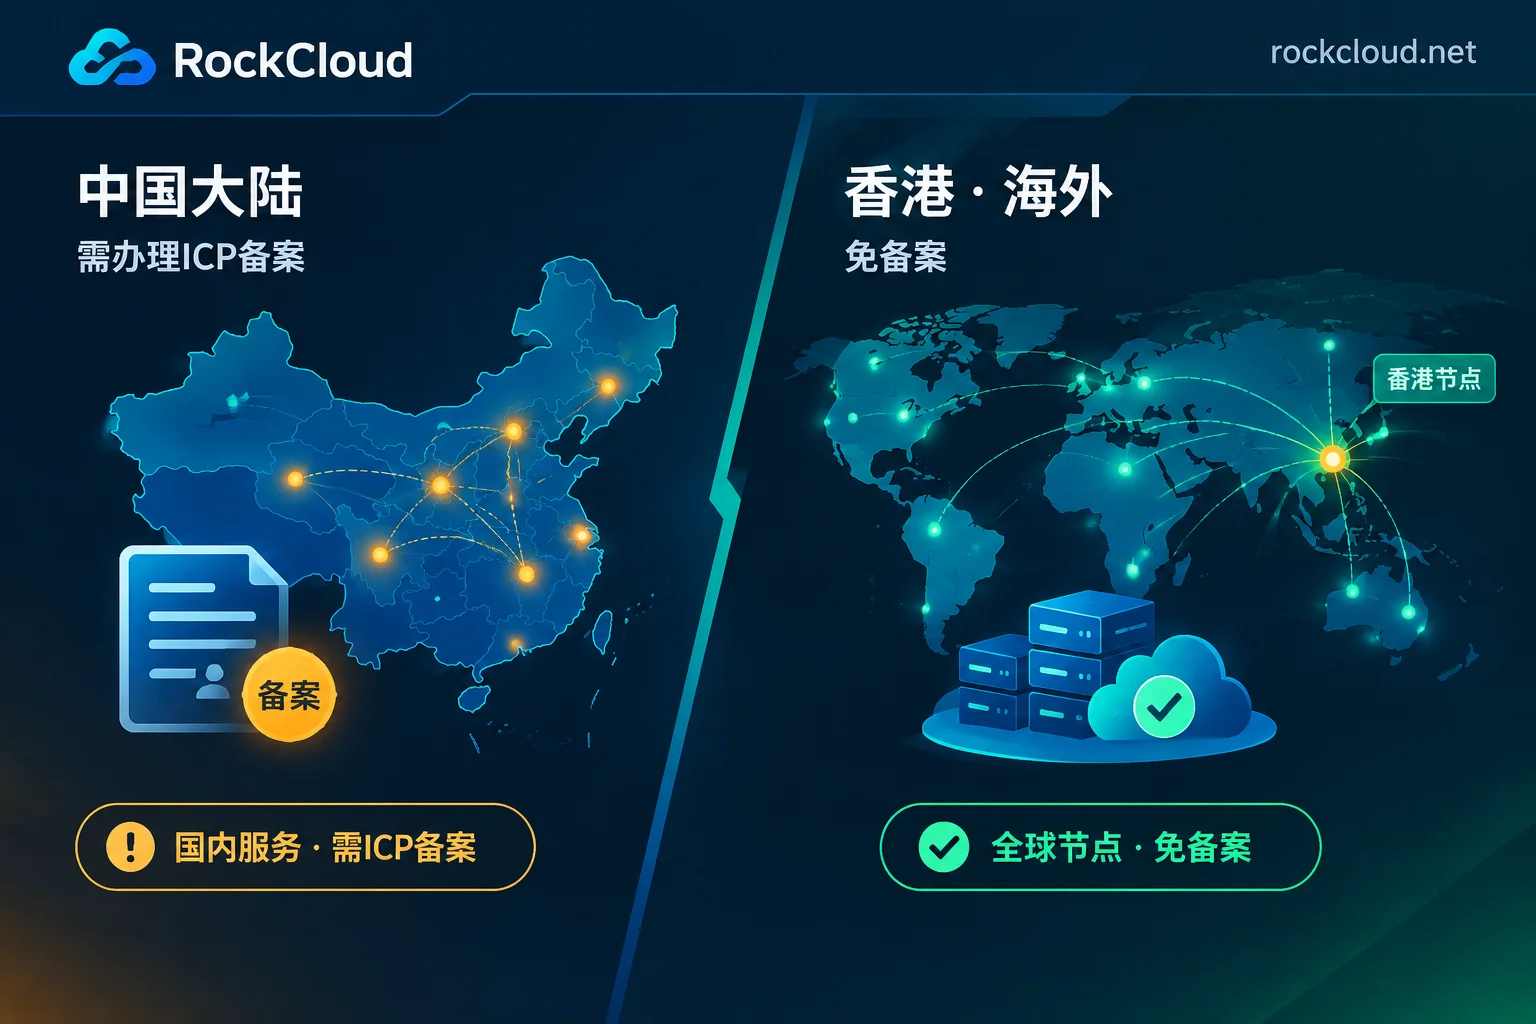
Does High-Defense CDN Require ICP Filing: Node Location Decides, No-Filing Access Solutions for Unregistered Domains
Whether a high-defense CDN requires ICP filing depends entirely on the physical location of its nodes, not on its protection capabilities. Using mainland China nodes requires an MIIT ICP filing, while using Hong Kong or overseas nodes allows access without filing. For unregistered domains or emergency protection, choosing Hong Kong/overseas nodes with CN2 direct connections is standard practice.
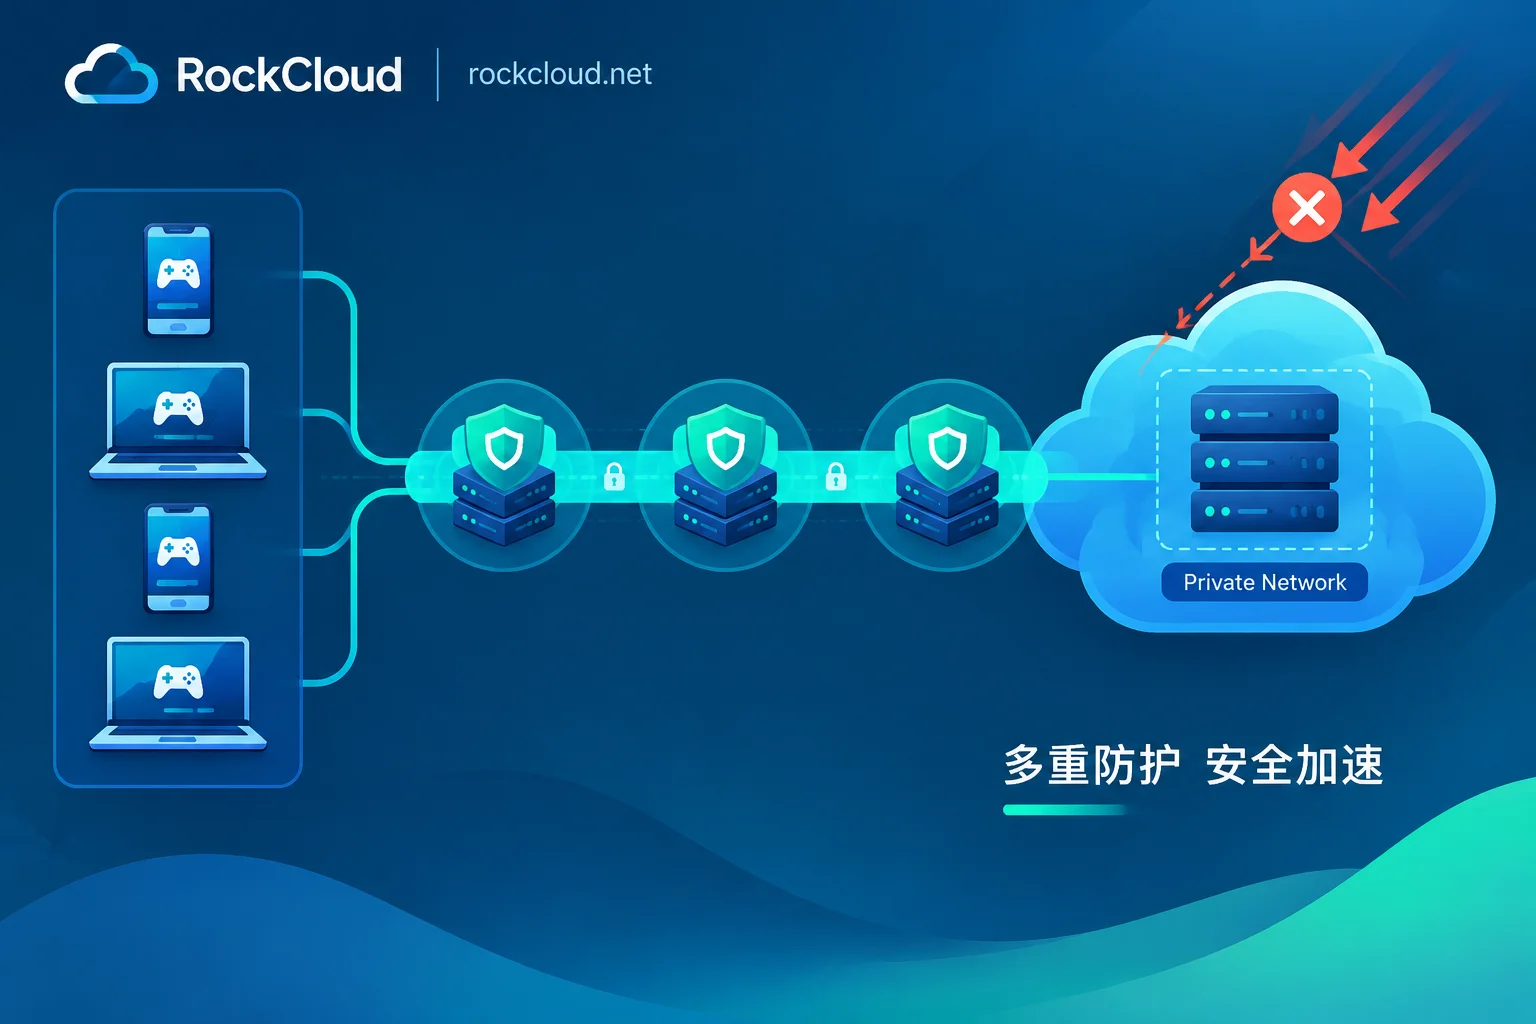
How to Hide Origin IP When a Card Game Server Is Attacked: Contain, Change IP, Encapsulate Access in Three Steps
When the origin IP is exposed, attacks bypass perimeter defenses and hit the server directly, sometimes leading to ISP blackholing. This article presents an operations-driven sequence: first contain the breach with security group whitelisting, then close all leak channels such as hardcoded client IPs, DNS history, and outbound callbacks, then change the public IP and move core nodes into a private network, and finally encapsulate access for long connections and web traffic separately through game shield and high-defense reverse proxy, with a mandatory post-change verification checklist.