RockCloud-基石云安全-官方博客
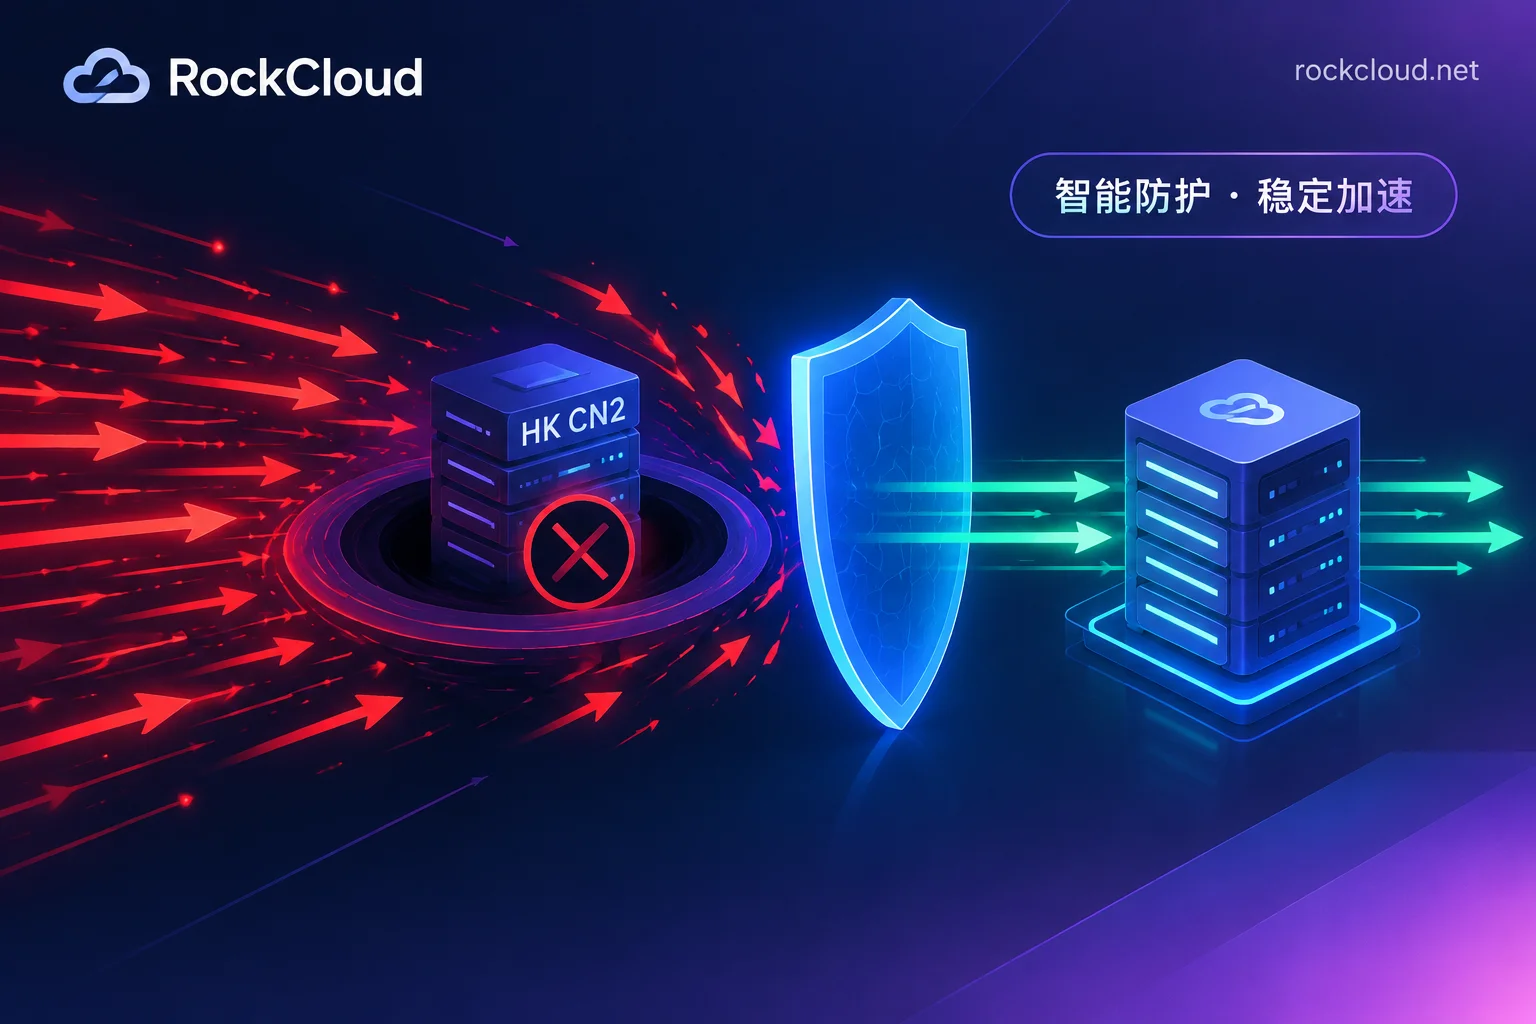
What to Do When a Hong Kong CN2 Server Is Hit by DDoS: Confirm Blackhole, Switch IP, Add Protection, Then Lock Down the Origin
Recovery sequence after a Hong Kong CN2 server is knocked offline by DDoS: check if it's in blackhole, decide whether to wait or change IP, add high-defense based on protocol, allow only origin-pull subnets at the origin, and finally audit IP leaks.
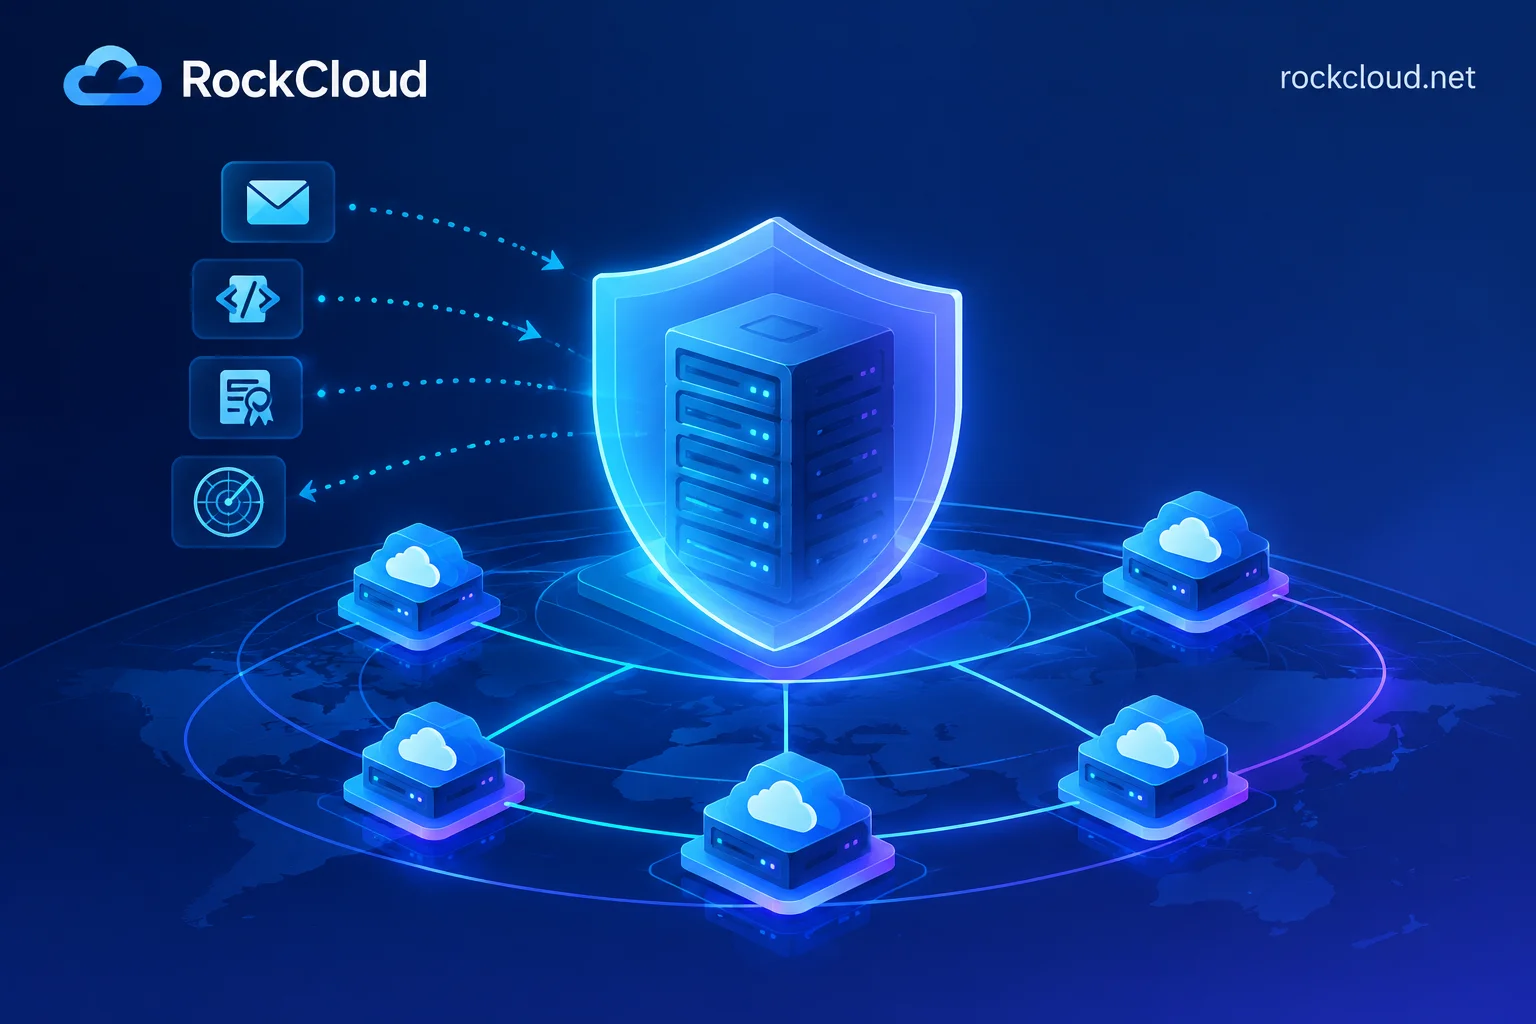
Will the Origin IP Still Be Exposed After Enabling a High-Defense CDN? Five Leak Paths, Hardening Order, and Post-Exposure Response
Even after enabling a high-defense CDN, the origin IP can still leak via historical DNS records, subdomains, email, certificate scans, and application outbound connections. This article provides self-check methods for each leak path, explains the hardening order such as origin whitelisting and default site blocking, and clarifies why you should plug the leaks first and then change the IP when the origin is under direct attack.
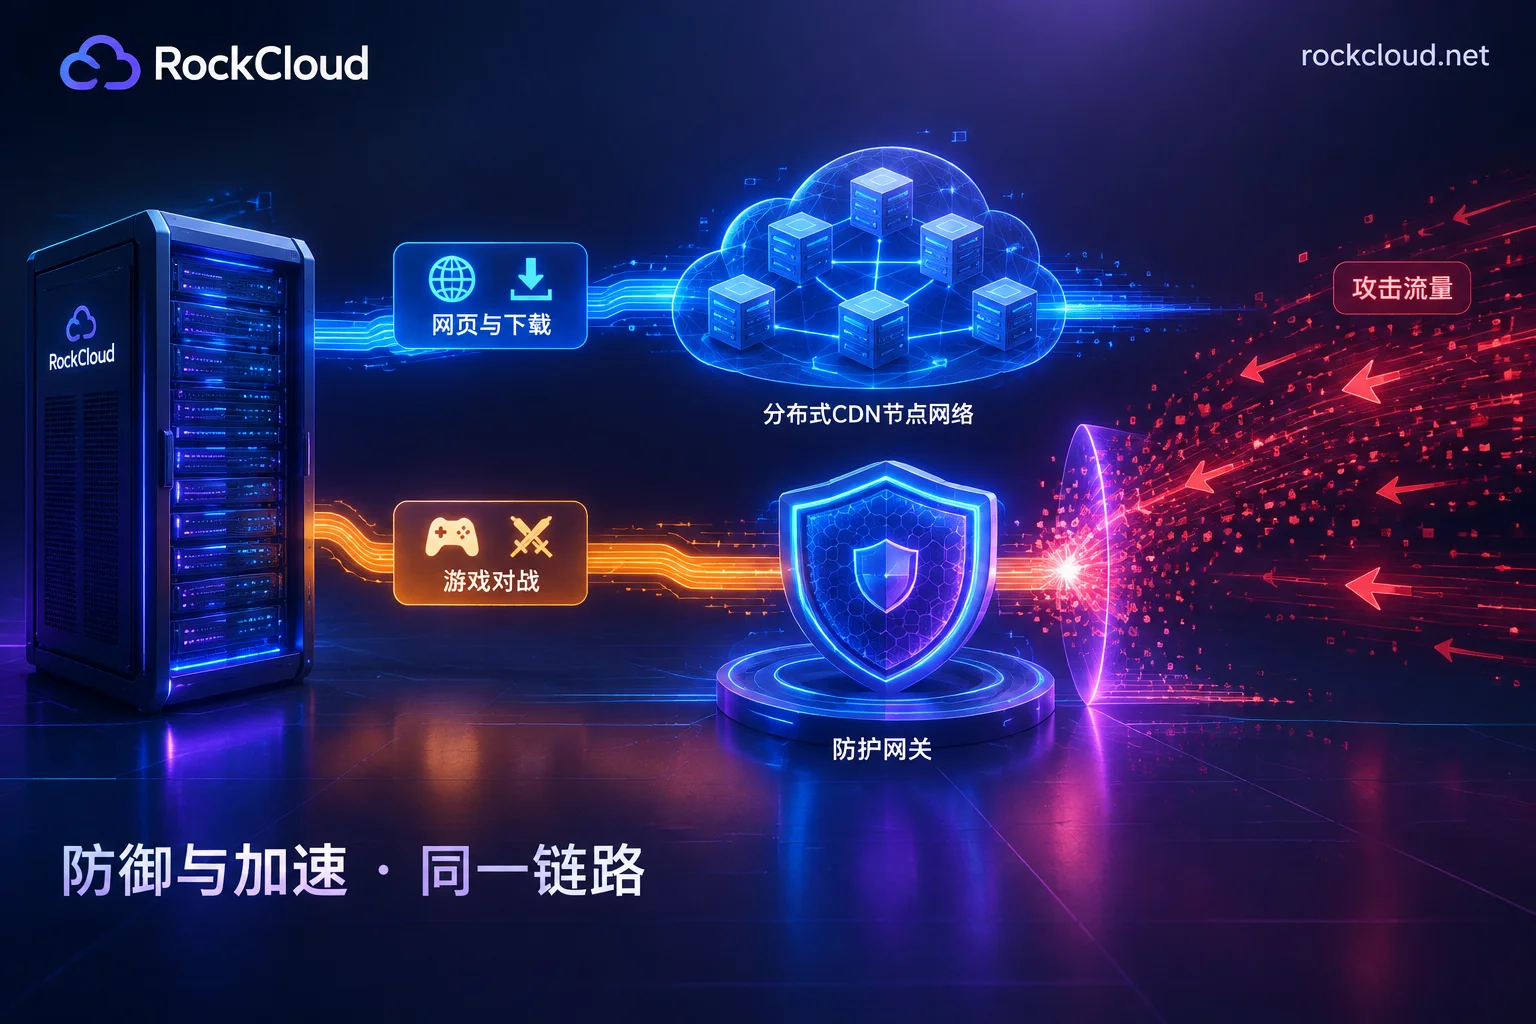
Game Servers: High-Defense IP or High-Defense CDN? Split Modules by Protocol and Layer Your Access
Most games don't need to choose between high-defense IP and high-defense CDN; this article splits game services by protocol into Web modules and real-time connection modules, explains which modules use high-defense CDN and which use high-defense IP or game shield, and provides key points for combined deployment and the access sequence when under attack.
Can High-Defense CDN Stop CC Attacks? How It Blocks, When It Fails, and Post-Setup Checks
High-defense CDN can stop CC attacks, but two conditions must be met: edge nodes must have Layer 7 scrubbing capabilities, and the origin must only be accessible via the CDN. This article explains the four methods high-defense CDN uses to block CC attacks, lists four common failure scenarios—origin IP exposure, dynamic interface penetration, challenge misfires, and non-HTTP traffic—and provides a post-setup self-check sequence and key questions to ask when choosing a provider.
In 2026, Hackers Have AI: DDoS Defense Gets Much Harder, But RockCloud Still Handles It Easily
In 2026, AI scripts paired with residential proxies make CC attacks look like real user traffic, and massive volumetric attacks often end within minutes—too fast for manual response. This article explains the signs of these new attacks in logs, the order of mitigation steps when under attack, and how to evaluate network-layer scrubbing, application-layer WAF, private protocol encapsulation, and billing models during selection.