RockCloud-基石云安全-官方博客
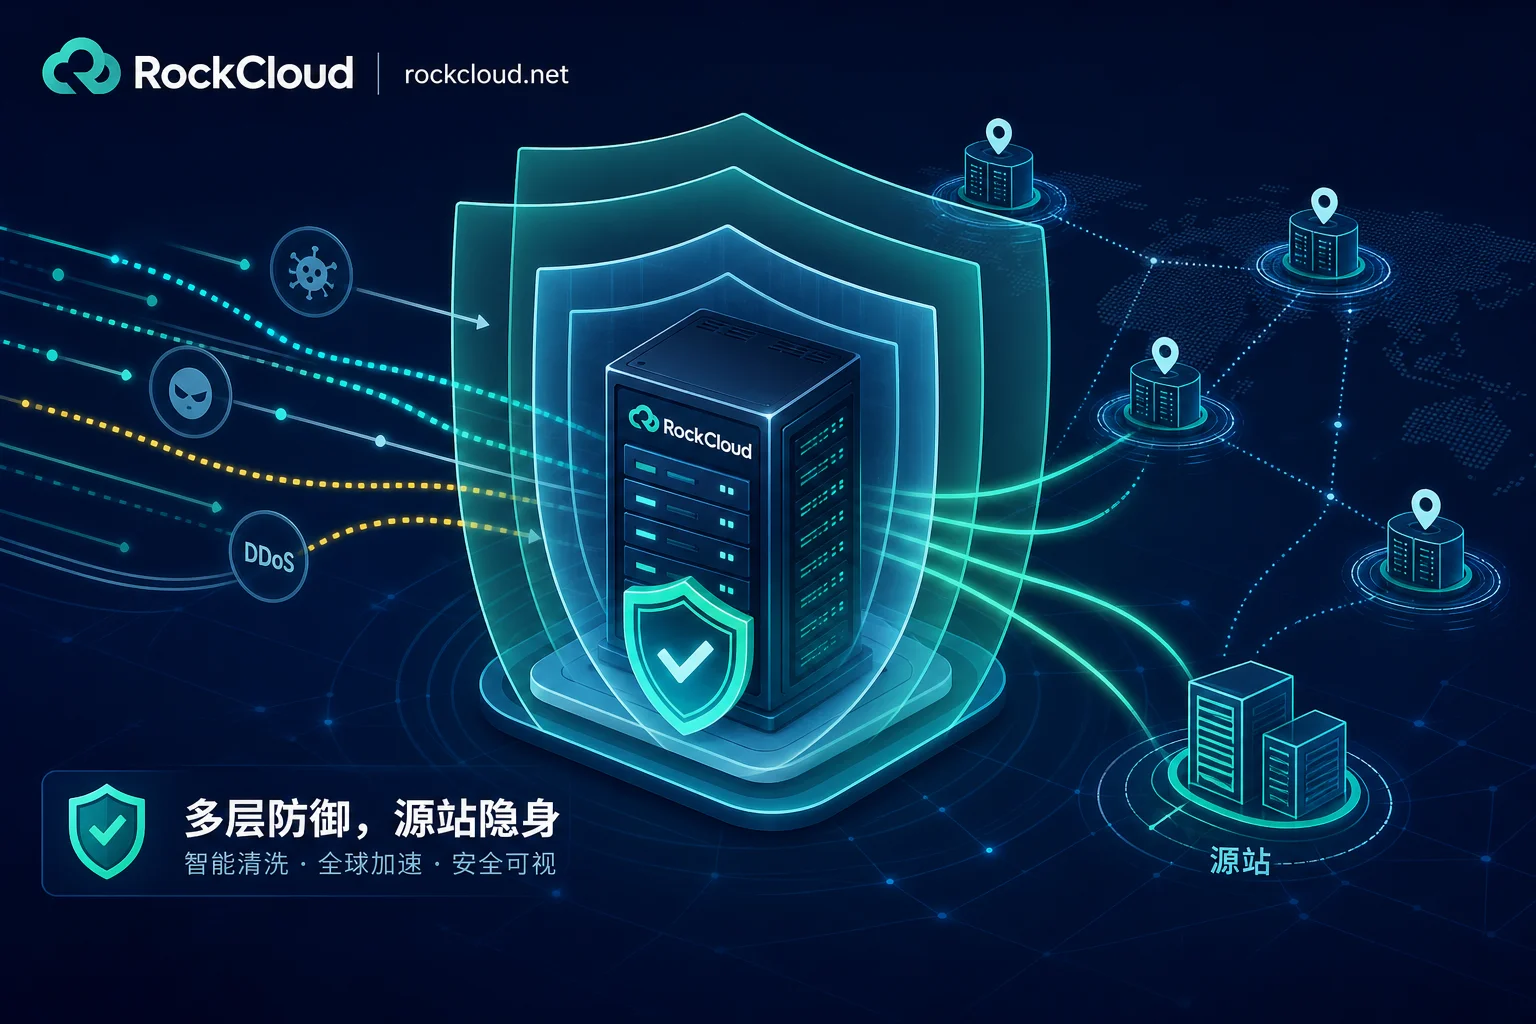
How to Hide Your Origin Server: 5 Defense Layers from Exposure to mTLS Origin Pull
Learn a 5-layer defense strategy to hide your origin server from direct attacks, covering exposure cleanup, DNS resolution lockdown, network whitelisting, mTLS authentication, and edge capacity.
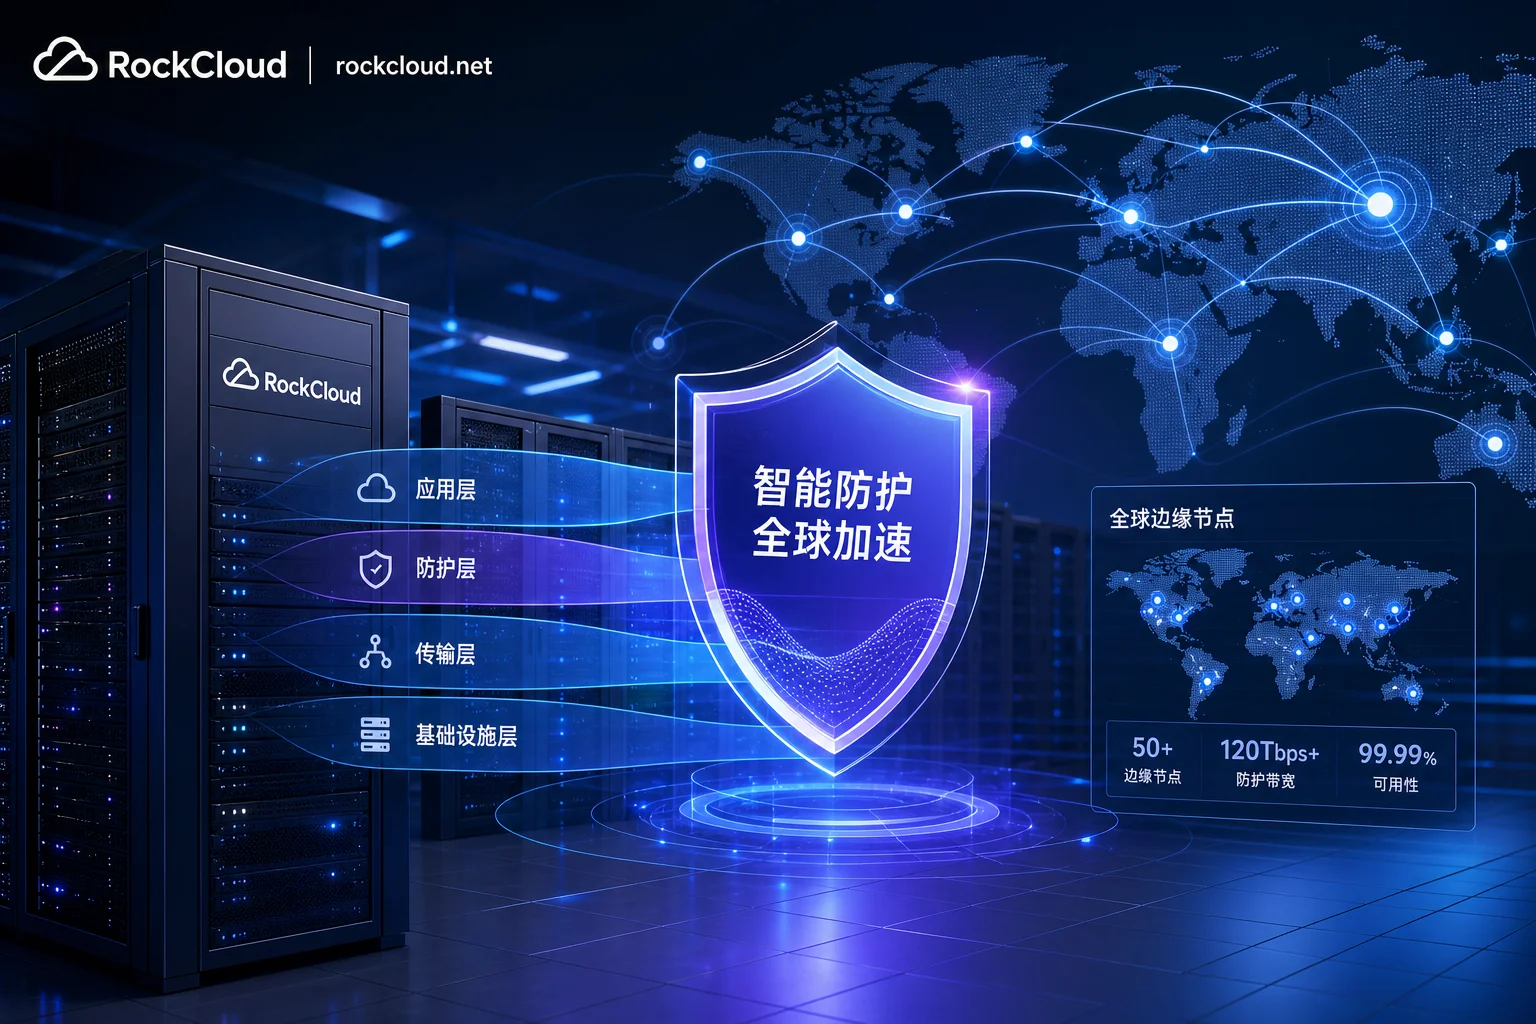
How to Choose CDN Security Acceleration? Key Points for Three-Layer Decision-Making and Verification
This article dissects the three-layer mechanisms of CDN security acceleration—capacity absorption, request buffering, and Layer-7 rules—from the dual decision chains of acceleration and security, and provides the root causes and verification checklists for origin servers being directly attacked.
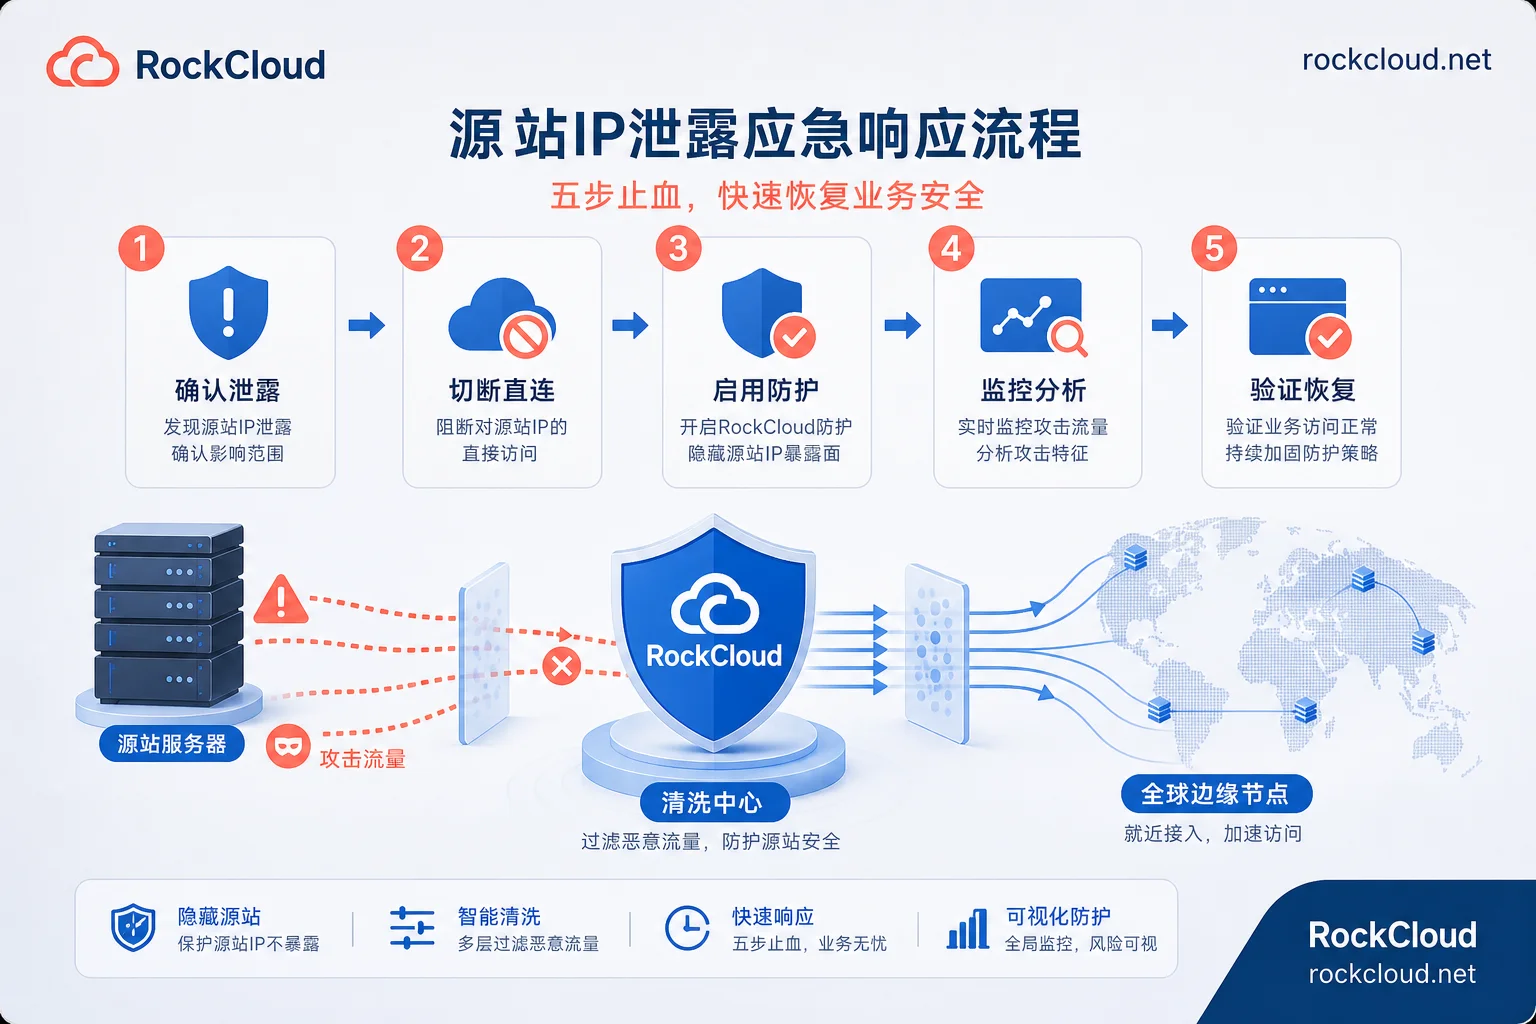
Emergency Response and Remediation Steps After Origin IP Leak: 5-Step Bleeding Control Sequence
Emergency response and remediation steps after origin IP leak: first use Step 0 to determine if the leak is real, then follow the five-step bleeding control sequence of 'containment → assessment → IP change → exposure fixation → verification'.